> initializing portfolio_

JEOSON LUNGSOD

// IT Assistant focused on cybersecurity — monitoring threats, analyzing traffic, and keeping systems locked down.

jeoson@portfolio: ~

$

> ./whoami --photo● live
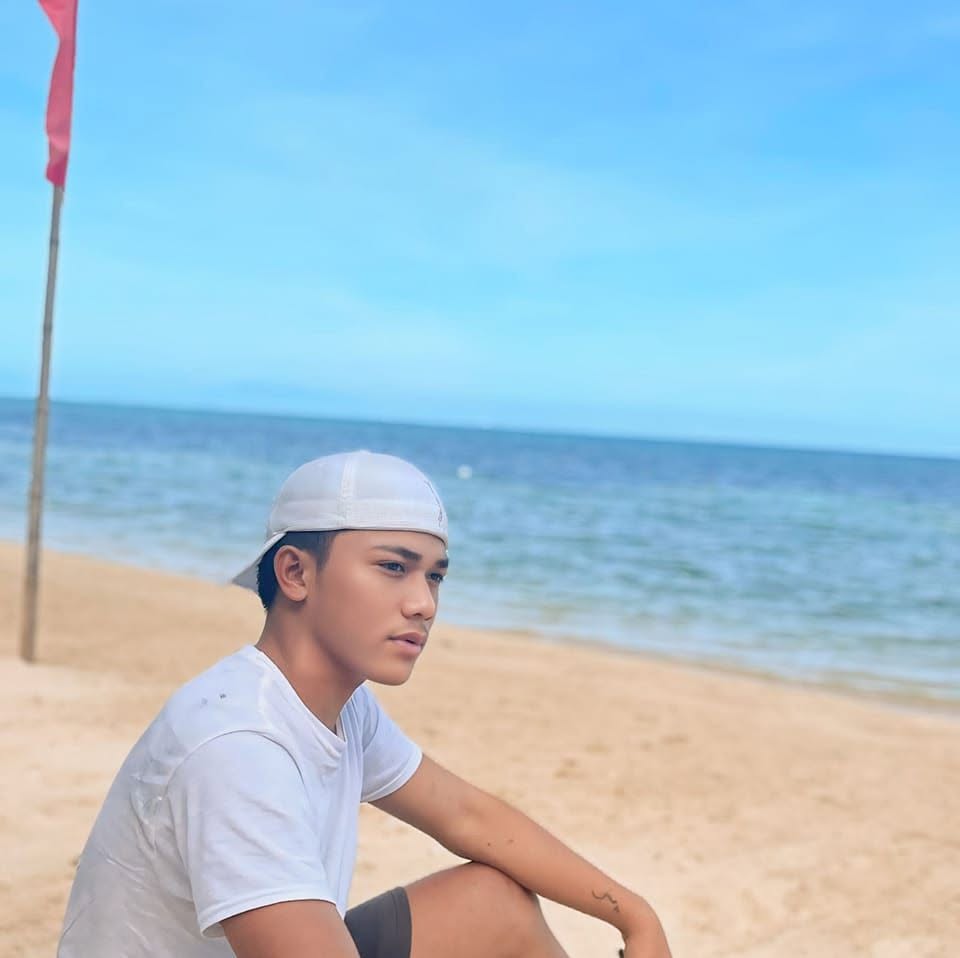
Jeoson Lungsod sitting on a beach, wearing a white cap and white t-shirt
subject: jeoson.lungsod · status: online
Cybersecurity focusOpen to work
01

About

I'm Jeoson — an IT assistant with a cybersecurity focus. I keep systems running smoothly and watch for anything that shouldn't be running at all.

My toolkit covers threat intelligence, network analysis and log monitoring — reputation lookups in VirusTotal, exposure checks in Shodan, packet captures in Wireshark, and hands-on security work in Kali Linux, all tied together in Splunk.

I'm open to work: IT support, SOC, and security-adjacent roles where both skill sets get used.

./profile --summary

name
Jeoson Lungsod
role
IT Assistant
focus
Cybersecurity
stack
VirusTotal · Shodan · Splunk · Wireshark · Kali
availability
Open to work
02

Skills

threat_intel

VirusTotalShodan

monitoring_analysis

SplunkWireshark

security_platforms

Kali Linux
03

Projects

[001]deploy: ok

Incident Reporting

CTM Quiz · Security Operations

Investigated a simulated Office 365 credential-theft incident and produced a structured high-severity incident ticket with a verified timeline, indicators of compromise, containment actions, and escalation steps.

  • Identified six malware and attack patterns, including ransomware, C2 beaconing, network scanning, adware, fileless malware, and a RAT.
  • Correlated one unauthorized login with 47 failed attempts from a malicious external IP.
  • Documented session revocation, password reset, IP blocking, and Tier 2 escalation.
Incident TicketingVirusTotalOffice 365Phishing Analysis
[010]deploy: ok

Critical Alert Triage

Operation Manila Fog · Full Escalation Simulation

Triaged a simulated active domain compromise involving a privileged login, rogue Domain Admin creation, and 2.1 GB of outbound data transfer from a domain controller.

  • Classified all three alerts as true positives and rated the incident Critical.
  • Mapped activity to T1078.002, T1136.002, T1098, and T1041.
  • Prepared an incident ticket and SBAR escalation with immediate isolation, account disablement, and IP-blocking recommendations.
SIEMEDRFirewall LogsMITRE ATT&CKSBAR
[011]deploy: ok

Splunk Security Analytics

BOTS v2 Security Overview

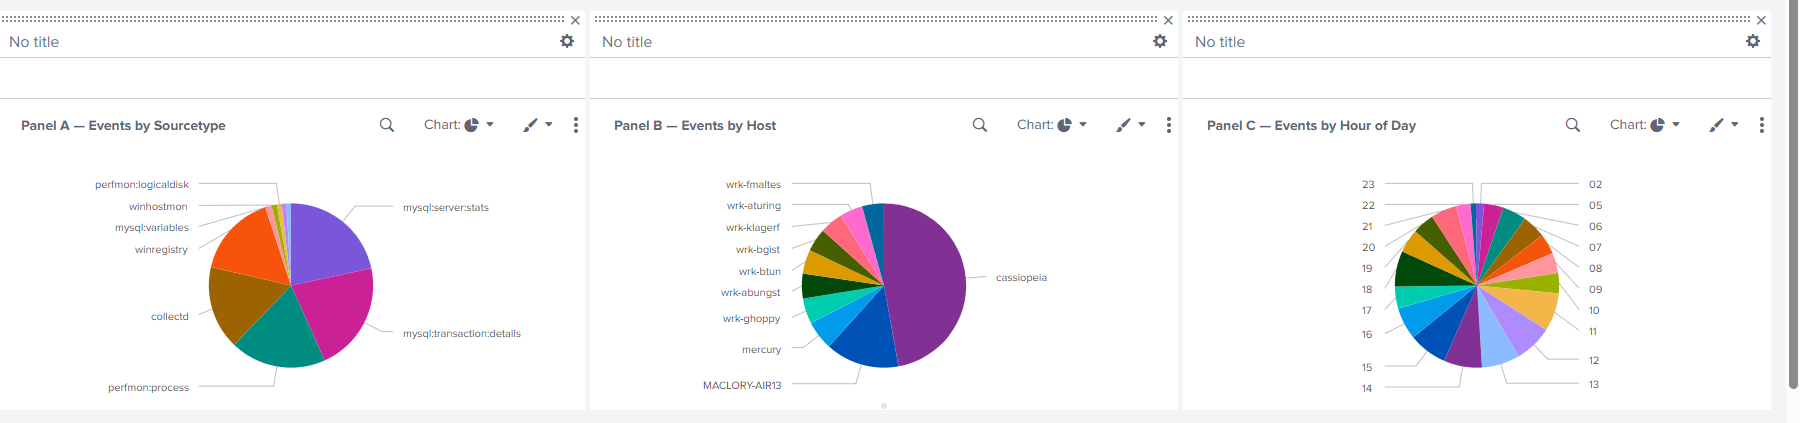
Built and reviewed a Splunk dashboard for the Boss of the SOC v2 dataset, turning high-volume security events into filterable visual summaries and searchable event evidence.

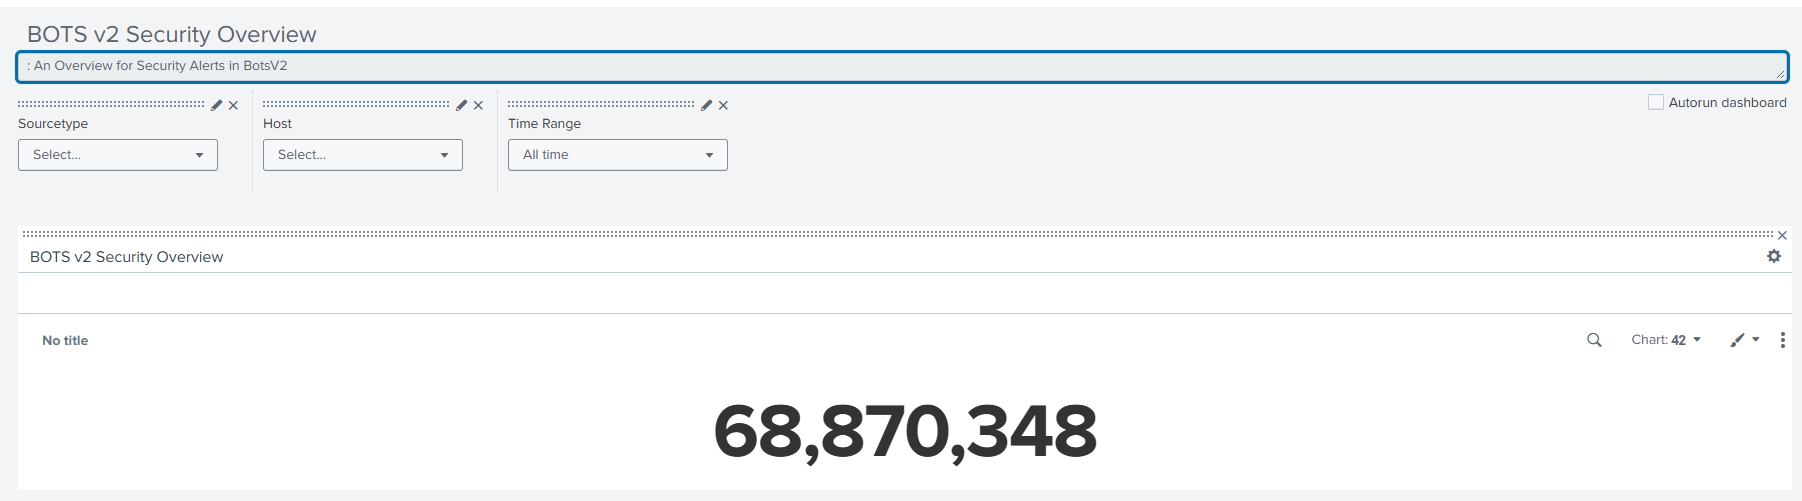
  • Summarized 68,870,348 events with filters for sourcetype, host, and time range.
  • Compared event distribution by sourcetype, host, and hour of day.
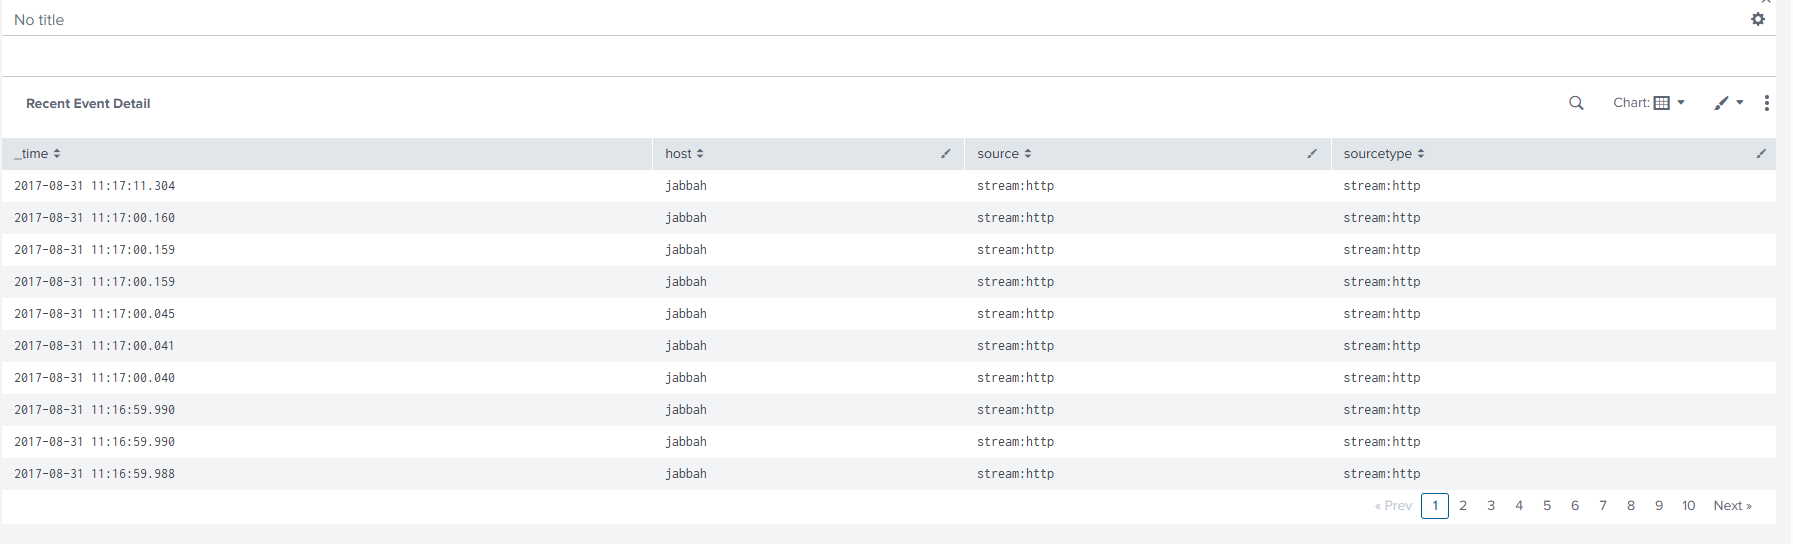
  • Reviewed recent HTTP event details across timestamp, host, source, and sourcetype fields.
Splunk dashboard with sourcetype, host, and time range filters showing a total of 68,870,348 events.
BOTS v2 Security Overview
Three pie charts showing events by sourcetype, events by host, and events by hour of day.
Panel A — Events by Sourcetype
Table of recent stream:http events from host jabbah with time, host, source, and sourcetype columns.
Recent Event Detail
SplunkBOTS v2SPLDashboardingLog Analysis
[100]deploy: ok

Cyber Threat Monitoring Project

Wireshark · Baselines & Anomaly Hunting

Completed a hands-on Wireshark threat-monitoring lab, moving from live packet capture and TCP handshake analysis to building a network baseline and hunting the traffic that did not belong.

  • Captured and analyzed a 24,719-packet live baseline, separating expected traffic such as QUIC, TLS, ARP, SSDP, and mDNS from deliberate activity.
  • Traced a web visit from DNS lookup through the TCP three-way handshake, HTTP requests, connection teardown, and a server-issued RST.
  • Wrote display filters for NXDOMAIN, resets, retransmissions, ICMP errors, TLS Client Hellos, and non-standard ports across a 363-packet hunt file.
  • Built a baseline dossier for a 45,218-packet office capture covering protocol mix, top talkers, external IPs, DNS rate, and scheduled NTP, update, and mDNS traffic.
  • Flagged cleartext HTTP credentials on a follow-up capture and mapped anomalies to MITRE ATT&CK techniques.
WiresharkPacket AnalysisDisplay FiltersTCP/IPNetwork BaseliningMITRE ATT&CK
[101]deploy: ok

Nmap Network Reconnaissance

Kali Linux · Metasploitable 2 Lab

Worked through six hands-on Nmap labs in an isolated VirtualBox network, progressing from host discovery to full service enumeration, scan-type comparison, and NSE script reconnaissance against intentionally vulnerable targets.

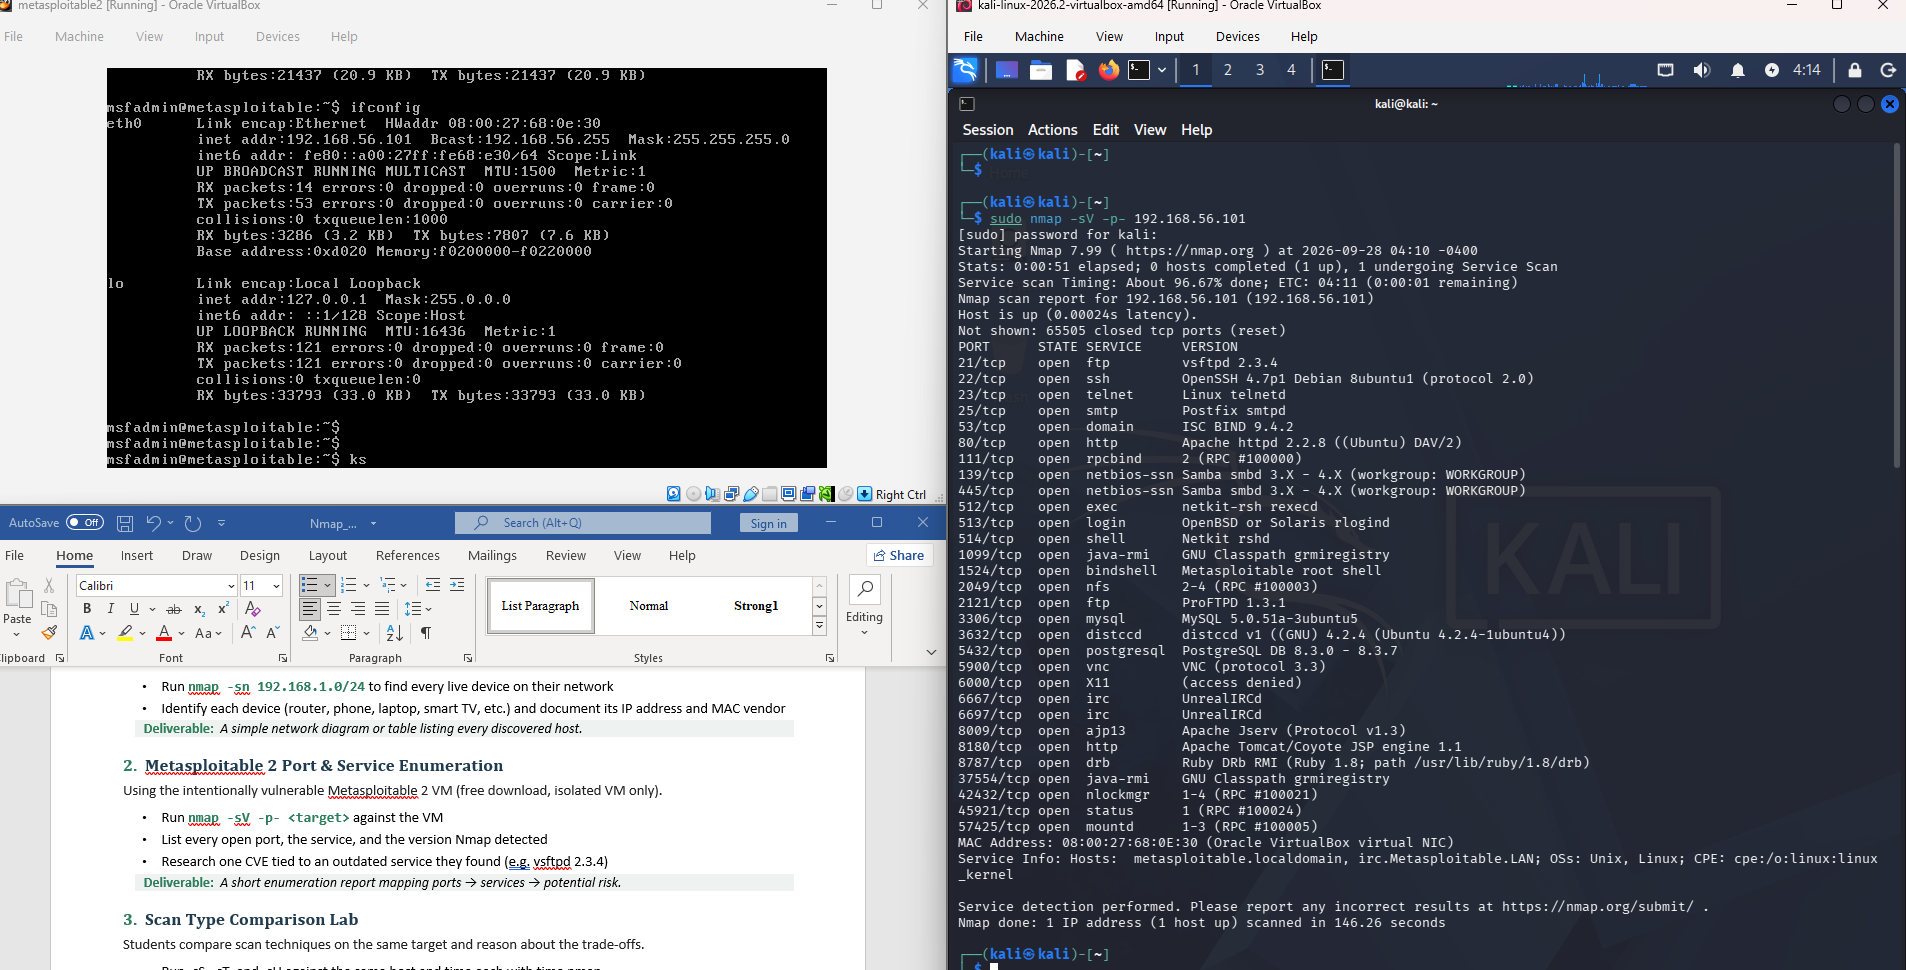
  • Ran a full-port service scan (nmap -sV -p-) against Metasploitable 2 and enumerated 30 open TCP ports with versions in 146 seconds.
  • Flagged outdated, high-risk services including vsftpd 2.3.4, UnrealIRCd, a bindshell on 1524, and Samba 3.x for CVE research.
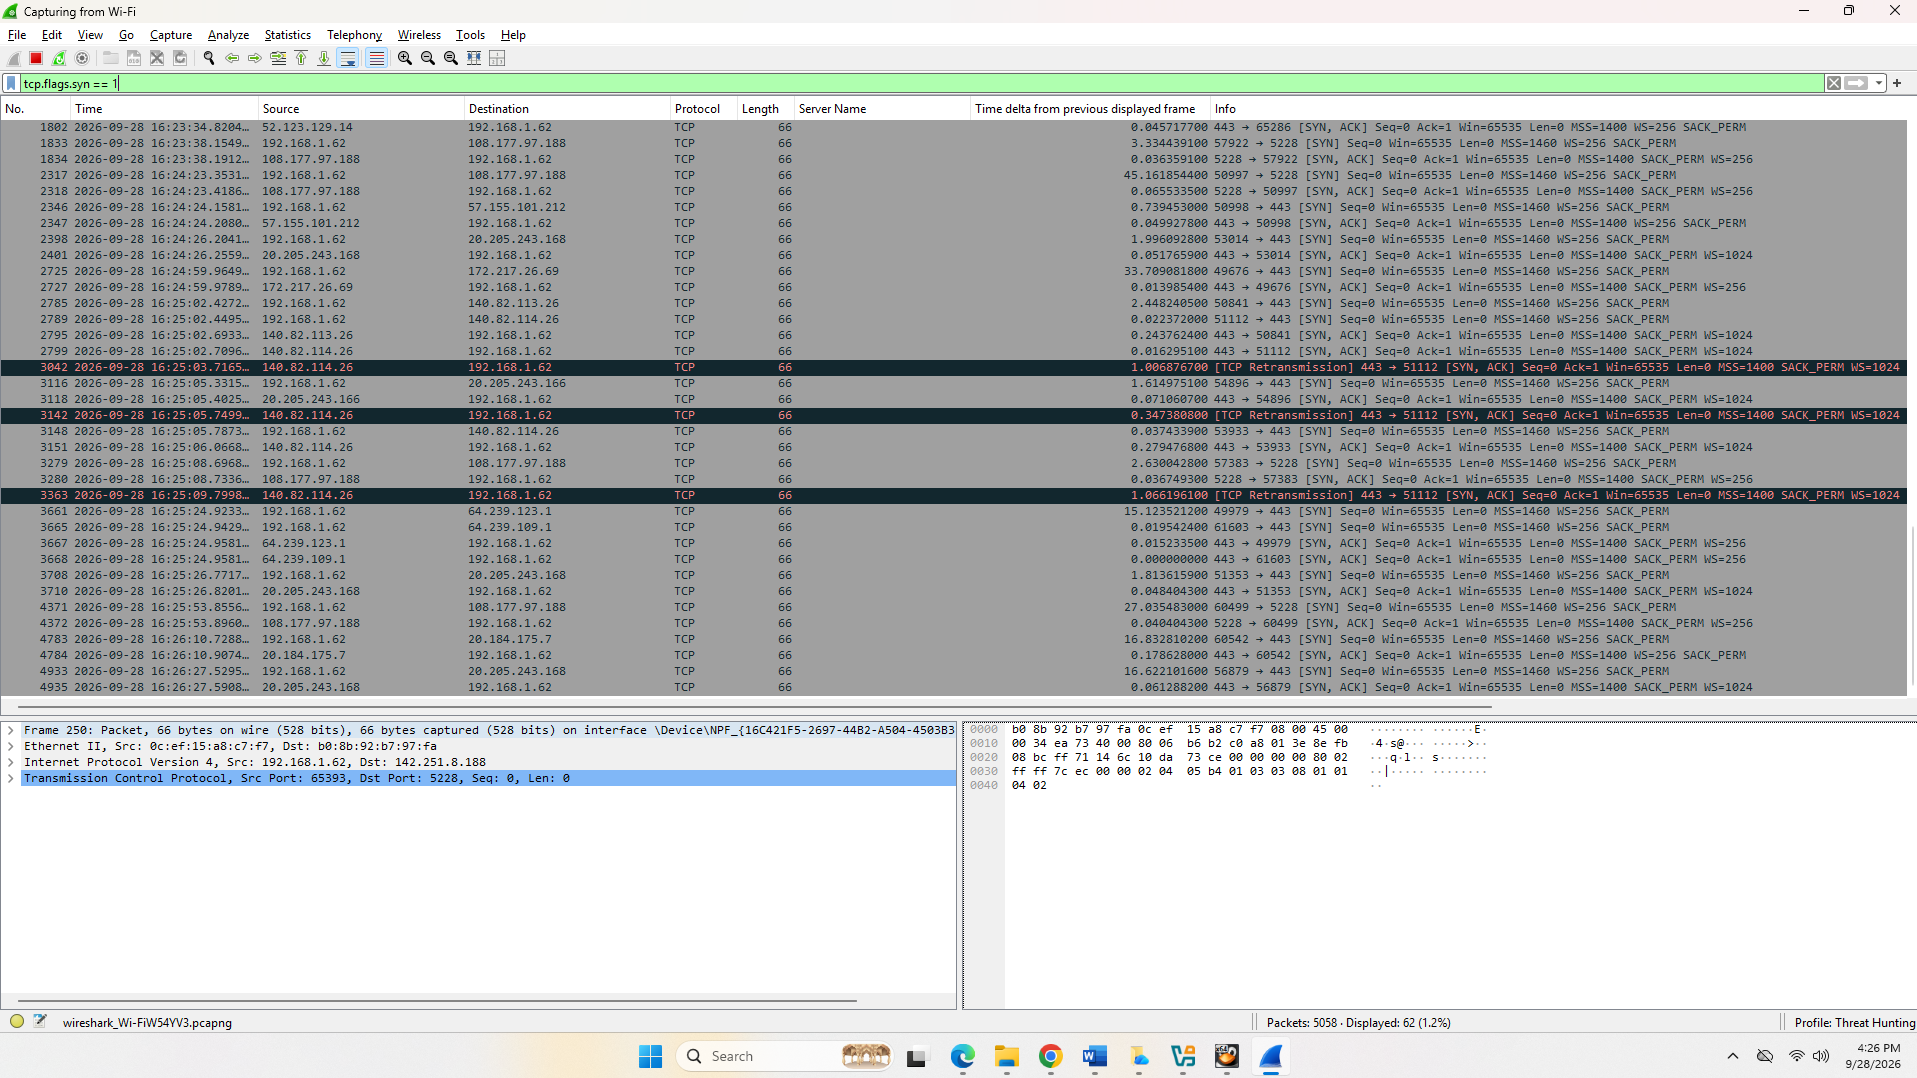
  • Compared -sS, -sT, and -sU scans while capturing traffic in Wireshark, isolating SYN and SYN/ACK behavior with tcp.flags.syn == 1.
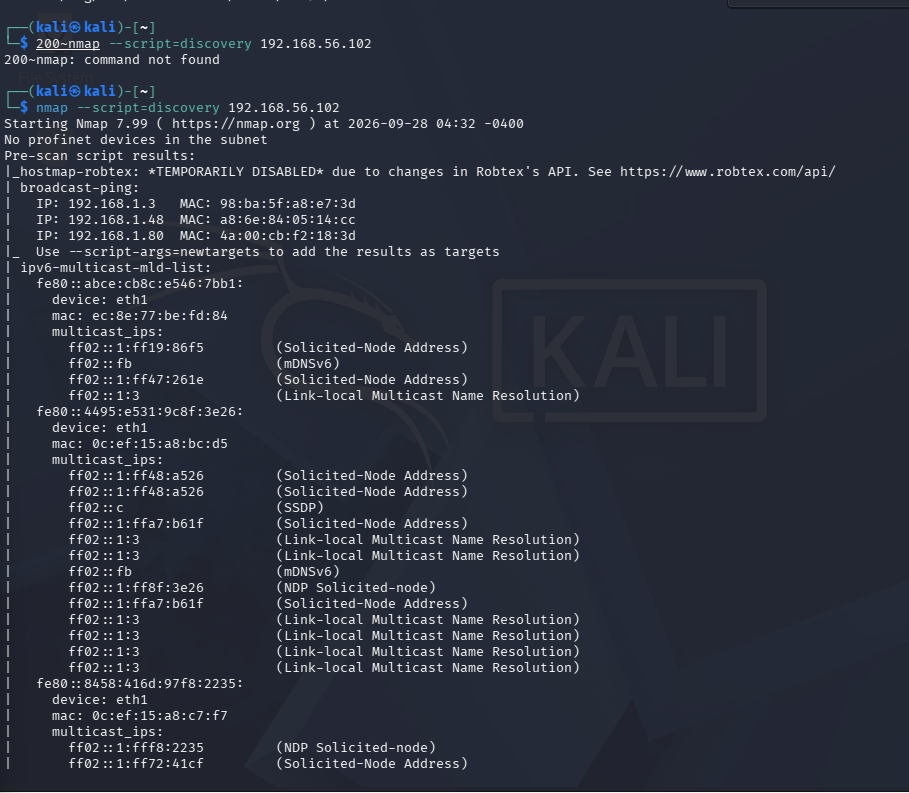
  • Used NSE discovery scripts to map broadcast-ping hosts, IPv6 multicast listeners, LLMNR, and SSDP activity on the lab subnet.
  • Kept all scanning inside a host-only lab network, following safe and authorized testing practice.
Kali Linux terminal showing nmap -sV -p- results against 192.168.56.101 listing open ports such as vsftpd 2.3.4, OpenSSH, Samba, and MySQL.
Service & Version Scan — Metasploitable 2
Wireshark capture filtered with tcp.flags.syn == 1 showing SYN and SYN/ACK packets and highlighted TCP retransmissions.
Scan Comparison — SYN Traffic in Wireshark
Terminal output of nmap --script=discovery showing broadcast-ping hosts and IPv6 multicast listener details.
NSE Discovery Script Results
NmapKali LinuxMetasploitable 2NSEWiresharkReconnaissance
04

Experience

IT Assistant

present
  • ›Triage suspicious files and URLs with VirusTotal reputation data.
  • ›Map exposed devices and services with Shodan network lookups.
  • ›Monitor logs and hunt anomalies in Splunk.
  • ›Capture and inspect network traffic with Wireshark.
  • ›Practice offensive and defensive security in Kali Linux.
05

Contact

Initialize contact_

Have a project, a role, or a hard problem? My inbox is always listening.